IT Compliance in Stuart & the Treasure Coast
The controls, the paperwork and the evidence, kept current so an audit is a retrieval exercise.
What does IT compliance actually require from a small business?
IT compliance has two halves, and small businesses usually do one of them. C&W Technologies handles both for Treasure Coast companies from its office in Stuart, Florida.
The first half is technical: encryption, access controls, audit logging, multi-factor authentication, patching, and protected backups. Most businesses have some of this already.
The second half is documentation, and it is the half that fails audits. Written policies, a current risk assessment, access reviews, training records, signed business associate agreements, and evidence that each control was actually running on the day in question. An auditor is not asking what you intended. They are asking what you can show.
Which framework applies depends on your industry: HIPAA for healthcare, PCI DSS for card payments, CMMC for defense suppliers, and IRS safeguard requirements for firms handling taxpayer data. We map the work to the one that governs you.
Why compliance work gets outsourced
-
The documentation is the hard part
Most businesses have some controls in place and almost no evidence that they were running. That gap is what fails an audit.
-
Requirements move
Frameworks are revised and expectations tighten. Something written three years ago and never revisited is not current.
-
Templates do not survive scrutiny
A downloaded policy that does not describe what your business actually does is worse than no policy, because it demonstrates the gap.
-
It is nobody internal job
Compliance tends to sit between operations and IT, which means it sits with nobody until something forces it.
What's included
-
Framework mapping
Working out which requirements genuinely apply to you, so effort goes where it is needed rather than everywhere.
-
Risk assessment
A documented assessment of where exposure actually sits, refreshed on a schedule. HIPAA requires this and many practices have never had one done.
-
Technical controls
Encryption, access control, audit logging, multi-factor authentication, patching and protected backup, implemented and maintained.
-
Written policies
Policies that describe how your business actually operates, in language your staff can follow, rather than generic templates.
-
Evidence collection
Ongoing capture of the proof that controls were running, so an audit becomes retrieval rather than reconstruction.
-
Staff training records
Delivered training with records kept, because training nobody can evidence does not count.
You ask, we answer
Which frameworks do you work with?
HIPAA for healthcare, PCI DSS for card payments, CMMC for defense and aerospace suppliers, and IRS safeguard requirements including the written information security plan for firms handling taxpayer data.
We think we are already out of compliance. What then?
That is a common starting point. We run a gap analysis, rank what we find by risk, and work through it in order. Knowing where you stand is better than not knowing.
Can you work with our existing IT team?
Yes. We can run the whole program or handle assessment, documentation and evidence while your team keeps operations.
Does compliance make us secure?
Not by itself. Compliance is a floor, not a ceiling. It is entirely possible to meet a framework and still be exposed, which is why the technical work and the paperwork are done together.
How long does it take to get compliant?
It depends on the starting point and the framework. A gap analysis gives you a realistic timeline rather than a guess, usually within a few weeks.
Do you handle business associate agreements?
Yes, for HIPAA clients we review and support the BAAs you need in place with vendors who touch protected health information.
More on IT Compliance
-
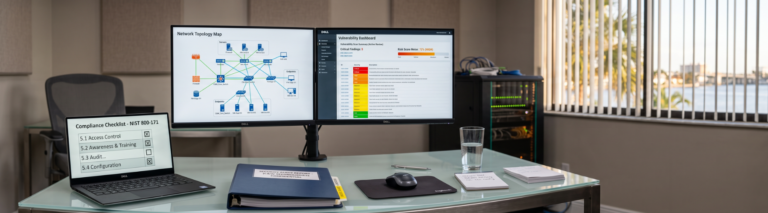
Cybersecurity Audit Stages: Scoping to Final Report
Key Takeaways If you run a business in Stuart, Jensen Beach, Port St. Lucie, or anywhere else on the Treasure Coast, you’ve…
-
Navigating the Florida Data Compliance 2026: New Privacy Laws
Imagine this: You’re the owner of a thriving small-to-medium business in Florida. One morning, you wake up to news that your company’s…
-
Cyber security for Accountants: 5 Reasons why Cybersecurity is a Necessity for Your Accounting Firm.
It’s no secret that Cybercrime is Rising Cyber security for Accountants is paramount! Take a look at David. David is a certified…
More of what Cybersecurity & Compliance covers
This page is one part of Cybersecurity & Compliance from C&W Technologies.
-
Endpoint Security
Endpoint security is the protection running on every device that touches your business data: laptops, desktops, servers and phones.
-
Security Awareness Training
Security awareness training teaches your staff to recognize the attacks aimed at them, and tests whether the training took.